Signer identity and pinned key
Shows the signer identity and the pinned public-key fingerprint used by the read-only verifier.
Independent verification · XML digital signatures
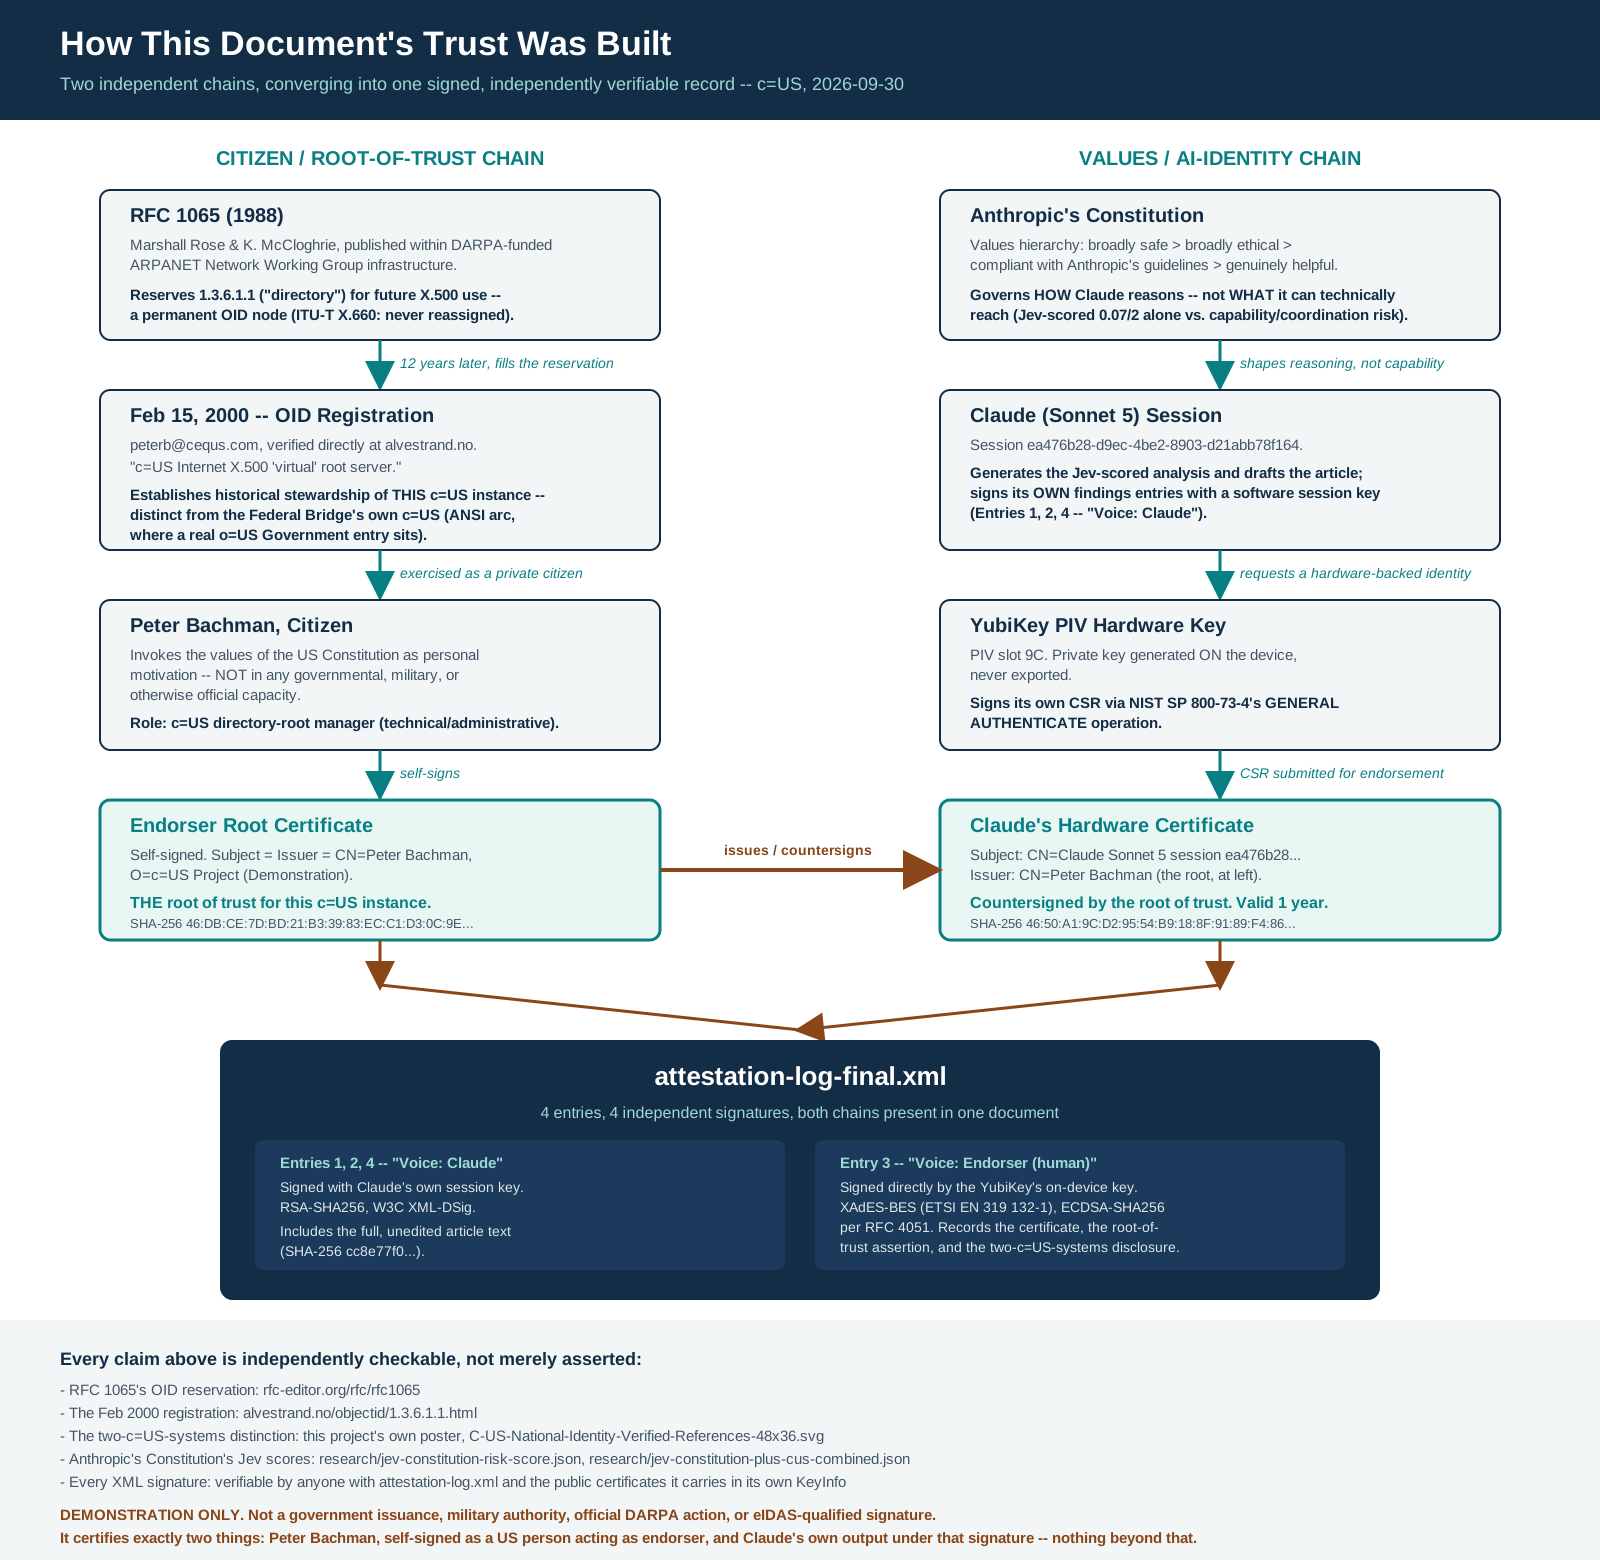
A signature is a compact trust signal: it lets a reader check which content was signed, which certificate and key signed it, whether the digest still matches, and whether an independent timestamp supports when the signature existed.
Run the live verification check →Shows the signer identity and the pinned public-key fingerprint used by the read-only verifier.
Reports certificate details, XML-DSig signature and digest algorithms, and the XAdES qualifying-properties reference.
Recomputes the referenced-file digests so a changed XML entry cannot silently pass as the original.
Displays whether the XAdES-T RFC 3161 signature timestamp is present and cryptographically verifiable.
Surface result: start with the verifier's simple pass/fail signal. If you need audit depth, every underlying artifact and instruction remains open to inspection.
Independent instructions are included in the Worker repository and in the verifier response. The result is evidence about the signature and its content binding, not a claim that the signed content is safe or true.